
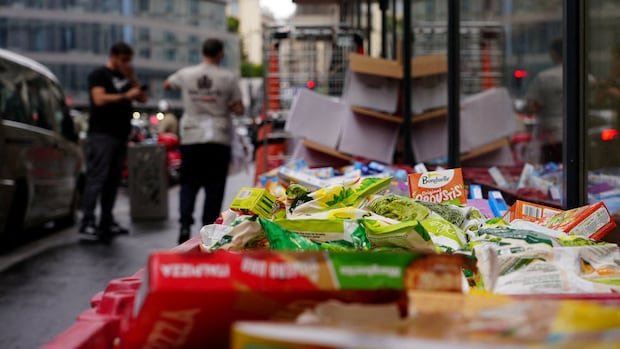

A recent cyberattack on French supermarkets resulted in the spoiling of food stored in hundreds of fridges, highlighting the vulnerabilities of internet-connected systems and devices, according to cybersecurity experts. The attack targeted centralized control systems that allowed hackers to remotely adjust fridge temperatures, causing significant food spoilage and potential fire hazards.
The Paris prosecutor’s office is investigating the cybercrime to determine the extent of the damage and identify the perpetrators. While no group has claimed responsibility or made ransom demands, the attack has raised concerns about the security and privacy of connected technologies.
The affected fridges in the stores were connected to the internet through a centralized control panel for remote monitoring and adjustment of temperature. The incident revealed a vulnerability in the control panels produced by companies like Danfoss, Copeland, and Dixell, leading to the compromise of numerous refrigeration systems.
Danfoss acknowledged that the affected units were running outdated firmware, making them susceptible to exploitation. A cybersecurity firm, Claroty, had previously reported a vulnerability in Danfoss’s firmware, emphasizing the importance of installing security patches promptly to prevent unauthorized access.
Such attacks on the food distribution system are not unprecedented. In the past, major companies like JBS and United Natural Foods, Inc. have experienced cyberattacks that disrupted their operations and caused significant shortages. These incidents underscore the growing threat posed by cybercriminals targeting critical infrastructure.
Experts warn that any device connected to the internet is potentially vulnerable to hacking, especially as more devices become digitally integrated. The convenience of centralized control systems comes with inherent security risks, necessitating continuous investment in cybersecurity measures to mitigate threats.
To enhance security, businesses and individuals are advised to prioritize safety-related updates, respond promptly to cyber incidents, and limit internet connectivity for devices where unnecessary. By taking proactive measures and staying vigilant, stakeholders can better protect against cyber threats targeting internet-connected devices.